

2025 Correct and Up-to-date CompTIA CAS-004 BrainDumps
Current CAS-004 dumps Preparation through Our Practice Test
CompTIA CAS-004 (CompTIA Advanced Security Practitioner (CASP+)) Exam is a certification program designed for advanced-level IT security practitioners. It is an internationally recognized certification that validates the skills and expertise of security professionals in developing and implementing effective cybersecurity solutions.
NEW QUESTION # 115
A web service provider has just taken on a very large contract that comes with requirements that are currently not being implemented in order to meet contractual requirements, the company must achieve the following thresholds
* 99 99% uptime
* Load time in 3 seconds
* Response time = <1 0 seconds
Starting with the computing environment, which of the following should a security engineer recommend to BEST meet the requirements? (Select THREE)
- A. Implementing server clusters
- B. Implementing RAID on the backup servers
- C. Ensuring technological diversity on critical servers
- D. Lowering storage input/output
- E. Utilizing redundant power for all developer workstations
- F. Deploying a content delivery network
- G. Employing bare-metal loading of applications
- H. Installing a firewall at corporate headquarters
Answer: A,D,F
Explanation:
To meet the contractual requirements of the web service provider, a security engineer should recommend the following actions:
Deploying a content delivery network (CDN): A CDN is a distributed system of servers that delivers web content to users based on their geographic location, the origin of the content, and the performance of the network. A CDN can help improve the uptime, load time, and response time of web services by caching content closer to the users, reducing latency and bandwidth consumption. A CDN can also help mitigate distributed denial-of-service (DDoS) attacks by absorbing or filtering malicious traffic before it reaches the origin servers, reducing the impact on the web service availability12.
Implementing server clusters: A server cluster is a group of servers that work together to provide high availability, scalability, and load balancing for web services. A server cluster can help improve the uptime, load time, and response time of web services by distributing the workload across multiple servers, reducing the risk of single points of failure and performance bottlenecks. A server cluster can also help recover from failures by automatically switching to another server in case of a malfunction34.
Lowering storage input/output (I/O): Storage I/O is the amount of data that can be read from or written to a storage device in a given time. Storage I/O can affect the performance of web services by limiting the speed of data transfer between the servers and the storage devices. Lowering storage I/O can help improve the load time and response time of web services by reducing the latency and congestion of data access. Lowering storage I/O can be achieved by using faster storage devices, such as solid-state drives (SSDs), optimizing the storage layout and configuration, such as using RAID or striping, and caching frequently accessed data in memory5 .
Installing a firewall at corporate headquarters is not a recommended action to meet the contractual requirements, as it does not directly affect the uptime, load time, or response time of web services. A firewall is a device or software that filters and blocks unwanted network traffic based on predefined rules. A firewall can help improve the security of web services by preventing unauthorized access and attacks, but it may also introduce additional latency and complexity to the network.
Employing bare-metal loading of applications is not a recommended action to meet the contractual requirements, as it does not directly affect the uptime, load time, or response time of web services. Bare-metal loading is a technique that allows applications to run directly on hardware without an operating system or a hypervisor. Bare-metal loading can help improve the performance and efficiency of applications by eliminating the overhead and interference of other software layers, but it may also increase the difficulty and cost of deployment and maintenance.
Implementing RAID on the backup servers is not a recommended action to meet the contractual requirements, as it does not directly affect the uptime, load time, or response time of web services. RAID (redundant array of independent disks) is a technique that combines multiple disks into a logical unit that provides improved performance, reliability, or both. RAID can help improve the availability and security of backup data by protecting it from disk failures or corruption, but it may also introduce additional complexity and overhead to the backup process.
Utilizing redundant power for all developer workstations is not a recommended action to meet the contractual requirements, as it does not directly affect the uptime, load time, or response time of web services. Redundant power is a technique that provides multiple sources of power for an IT system in case one fails. Redundant power can help improve the availability and reliability of developer workstations by preventing them from losing power due to outages or surges, but it may also increase the cost and energy consumption of the system.
Ensuring technological diversity on critical servers is not a recommended action to meet the contractual requirements, as it does not directly affect the uptime, load time, or response time of web services. Technological diversity is a technique that uses different types of hardware, software, or platforms in an IT environment. Technological diversity can help improve resilience by reducing single points of failure and increasing compatibility, but it may also introduce additional complexity and inconsistency to the environment. Reference: What Is CDN? How Does CDN Work? | Imperva, What Is Server Clustering? | IBM, What Is Server Clustering? | IBM, Server Clustering: What It Is & How It Works | Liquid Web, Storage I/O Performance - an overview | ScienceDirect Topics, [How to Improve Storage I/O Performance | StarWind Blog], [What Is Firewall Security? | Cisco], [What is Bare Metal? | IBM], [What is RAID? | Dell Technologies US], [What Is Redundant Power Supply? | Dell Technologies US], [Technological Diversity - an overview | ScienceDirect Topics]
NEW QUESTION # 116
A company is looking to fortify its cybersecurity defenses and is focusing on its network infrastructure. The solution cannot affect the availability of the company's services to ensure false positives do not drop legitimate traffic.
Which of the following would satisfy the requirement?
- A. NIPS
- B. WAF
- C. NIDS
- D. Reverse proxy
Answer: A
NEW QUESTION # 117
A company has been the target of LDAP injections, as well as brute-force, whaling, and spear-phishing attacks. The company is concerned about ensuring continued system access. The company has already implemented a SSO system with strong passwords. Which of the following additional controls should the company deploy?
- A. Two-factor authentication
- B. Identity proofing
- C. Live identity verification
- D. Challenge questions
Answer: A
Explanation:
While the company has implemented Single Sign-On (SSO) with strong passwords, additional security controls are required to mitigate attacks such as LDAP injections, brute-force, whaling, and spear-phishing.
Two-factor authentication (2FA) provides an additional layer of security by requiring users to provide two different forms of authentication (e.g., a password and a security token or a biometric factor), reducing the likelihood of unauthorized access even if passwords are compromised. CASP+ emphasizes the importance of using multi-factor authentication mechanisms to strengthen access control and protect against such attacks.
References:
* CASP+ CAS-004 Exam Objectives: Domain 2.0 - Enterprise Security Operations (Access Control and Multi-factor Authentication)
* CompTIA CASP+ Study Guide: Implementing Two-Factor Authentication for System Access
NEW QUESTION # 118
Real-time, safety-critical systems MOST often use serial busses that:
- A. have non-deterministic behavior and are not deployed with encryption.
- B. have deterministic behavior and are deployed with encryption.
- C. have deterministic behavior and are not deployed with encryption.
- D. have non-deterministic behavior and are deployed with encryption.
Answer: C
Explanation:
For safety-critical systems, CAN is the most widely used communication protocol and does not have a built-in encryption mechanism. This prioritizes low latency and deterministic response times over encryption.
NEW QUESTION # 119
A satellite communications ISP frequently experiences outages and degraded modes of operation over one of its legacy satellite links due to the use of deprecated hardware and software. Three days per week, on average, a contracted company must follow a checklist of 16 different high-latency commands that must be run in serial to restore nominal performance. The ISP wants this process to be automated.
Which of the following techniques would be BEST suited for this requirement?
- A. Provide the contractors with direct access to satellite telemetry data.
- B. Deploy SOAR utilities and runbooks.
- C. Reduce link latency on the affected ground and satellite segments.
- D. Replace the associated hardware.
Answer: B
NEW QUESTION # 120
A security analyst discovered that a database administrator's workstation was compromised by malware. After examining the Jogs. the compromised workstation was observed connecting to multiple databases through ODBC. The following query behavior was captured: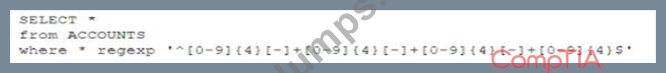
Assuming this query was used to acquire and exfiltrate data, which of the following types of data was compromised, and what steps should the incident response plan contain?
A) Personal health information: Inform the human resources department of the breach and review the DLP logs.
#) Account history; Inform the relationship managers of the breach and create new accounts for the affected users.
C) Customer IDs: Inform the customer service department of the breach and work to change the account numbers.
D) PAN: Inform the legal department of the breach and look for this data in dark web monitoring.
- A. Option D
- B. Option C
- C. Option A
- D. Option B
Answer: A
NEW QUESTION # 121
Company A is establishing a contractual with Company B. The terms of the agreement are formalized in a document covering the payment terms, limitation of liability, and intellectual property rights. Which of the following documents will MOST likely contain these elements
- A. Company A-B SLA v2.docx
- B. Company A MSA v3.docx
- C. Company A OLA v1b.docx
- D. Company A MOU v1.docx
- E. Company A-B NDA v03.docx
Answer: B
Explanation:
A MSA stands for master service agreement, which is a document that covers the general terms and conditions of a contractual relationship between two parties. It usually includes payment terms, limitation of liability, intellectual property rights, dispute resolution, and other clauses that apply to all services provided by one party to another. Verified References: https://www.comptia.org/training/books/casp-cas-004-study- guide , https://www.upcounsel.com/master-service-agreement
NEW QUESTION # 122
A security architect was asked to modify an existing internal network design to accommodate the following requirements for RDP:
* Enforce MFA for RDP
* Ensure RDP connections are only allowed with secure ciphers.
The existing network is extremely complex and not well segmented. Because of these limitations, the company has requested that the connections not be restricted by network-level firewalls Of ACLs.
Which of the following should the security architect recommend to meet these requirements?
- A. Implement a bastion host with a secure cipher configuration enforced.
- B. Implement a remote desktop gateway server, enforce secure ciphers, and configure to use OTP
- C. Implement a reverse proxy for remote desktop with a secure cipher configuration enforced.
- D. Implement a GPO that enforces TLS cipher suites and limits remote desktop access to only VPN users.
Answer: B
Explanation:
A remote desktop gateway server is a solution that allows users to connect to remote desktops or applications over the internet using the Remote Desktop Protocol (RDP). A remote desktop gateway server can enforce MFA for RDP by integrating with Azure AD MFA using the Network Policy Server (NPS) extension. The NPS extension can send anOTP (one-time password) to the user's phone or mobile app as a second factor of authentication. A remote desktop gateway server can also enforce secure ciphers by configuring the SSL Cipher Suite Order Group Policy setting to specify the preferred order of cipher suites for TLS/SSL connections. Verified References:
* https://docs.microsoft.com/en-us/windows-server/remote/remote-desktop-services/rds-plan-access-from-an
* https://docs.microsoft.com/en-us/azure/active-directory/authentication/howto-mfa-nps-extension-rdg
* https://docs.microsoft.com/en-us/windows-server/security/tls/tls-registry-settings#ssl-cipher-suite-order
NEW QUESTION # 123
A security analyst is investigating a series of suspicious emails by employees to the security team. The email appear to come from a current business partner and do not contain images or URLs. No images or URLs were stripped from the message by the security tools the company uses instead, the emails only include the following in plain text.
Which of the following should the security analyst perform?
- A. Contact the security department at the business partner and alert them to the email event.
- B. Block the IP address for the business partner at the perimeter firewall.
- C. Pull the devices of the affected employees from the network in case they are infected with a zero-day virus.
- D. Configure the email gateway to automatically quarantine all messages originating from the business partner.
Answer: A
NEW QUESTION # 124
In support of disaster recovery objectives, a third party agreed to provide 99.999% uptime.
Recently, a hardware failure impacted a firewall without service degradation. Which of the following resiliency concepts was most likely in place?
- A. High availability
- B. Replication
- C. Redundancy
- D. Clustering
Answer: A
Explanation:
High availability ensures continuous operation despite hardware failures by leveraging redundant components like clustered firewalls or failover systems.
NEW QUESTION # 125
A security analyst is reading the results of a successful exploit that was recently conducted by third-party penetration testers. The testers reverse engineered a privileged executable. In the report, the planning and execution of the exploit is detailed using logs and outputs from the test However, the attack vector of the exploit is missing, making it harder to recommend remediation's. Given the following output: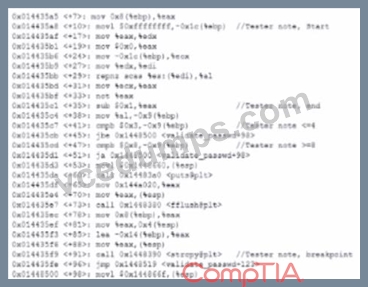
The penetration testers MOST likely took advantage of:
- A. An integer overflow vulnerability
- B. A plain-text password disclosure
- C. A buffer overflow vulnerability
- D. A TOC/TOU vulnerability
Answer: D
NEW QUESTION # 126
A new security policy states all wireless and wired authentication must include the use of certificates when connecting to internal resources within the enterprise LAN by all employees.
Which of the following should be configured to comply with the new security policy? (Choose two.)
- A. OAuth
- B. SSO
- C. Push-based authentication
- D. New pre-shared key
- E. 802.1X
- F. PKI
Answer: E,F
NEW QUESTION # 127
A small company needs to reduce its operating costs. vendors have proposed solutions, which all focus on management of the company's website and services. The Chief information Security Officer (CISO) insist all available resources in the proposal must be dedicated, but managing a private cloud is not an option. Which of the following is the BEST solution for this company?
- A. Single-tenancy SaaS
- B. Multinency SaaS
- C. Community cloud service model
- D. On-premises cloud service model
Answer: A
Explanation:
Explanation
A single-tenancy SaaS solution is the best solution for this company. SaaS stands for software as a service, which is a cloud-based model that allows customers to access applications hosted by a provider over the internet. A single-tenancy SaaS solution means that the company has its own dedicated instance of the application and its underlying infrastructure, which offers more control, customization, and security than a multi-tenancy SaaS solution where multiple customers share the same resources. A single-tenancy SaaS solution also eliminates the need for managing a private cloud or an on-premises infrastructure. Verified References: https://www.comptia.org/training/books/casp-cas-004-study-guide ,
https://www.ibm.com/cloud/learn/saas
NEW QUESTION # 128
A shipping company that is trying to eliminate entire classes of threats is developing an SELinux policy to ensure its custom Android devices are used exclusively for package tracking.
After compiling and implementing the policy, in which of the following modes must the company ensure the devices are configured to run?
- A. Enforcing
- B. Mandatory
- C. Permissive
- D. Protecting
Answer: A
Explanation:
Reference: https://source.android.com/security/selinux/customize
SELinux (Security-Enhanced Linux) is a security module for Linux systems that provides mandatory access control (MAC) policies for processes and files. SELinux can operate in three modes:
Enforcing: SELinux enforces the MAC policies and denies access based on rules.
Permissive: SELinux does not enforce the MAC policies but only logs actions that would have been denied if running in enforcing mode.
Disabled: SELinux is turned off.
To ensure its custom Android devices are used exclusively for package tracking, the company must configure SELinux to run in enforcing mode. This mode will prevent any unauthorized actions or applications from running on the devices and protect them from potential threats or misuse. References:
https://access.redhat.com/documentation/en-us/red_hat_enterprise_linux/7/html/selinux_users_and_administrato
https://source.android.com/security/selinux
NEW QUESTION # 129
A home automation company just purchased and installed tools for its SOC to enable incident identification and response on software the company develops. The company would like to prioritize defenses against the following attack scenarios:
- Unauthorized insertions into application development environments
- Authorized insiders making unauthorized changes to environment
configurations
Which of the following actions will enable the data feeds needed to detect these types of attacks on development environments? (Choose two.)
- A. Model user behavior and monitor for deviations from normal.
- B. Monitor dependency management tools and report on susceptible third-party libraries.
- C. Implement an XML gateway and monitor for policy violations.
- D. Install an IDS on the development subnet and passively monitor for vulnerable services.
- E. Continuously monitor code commits to repositories and generate summary logs.
- F. Perform static code analysis of committed code and generate summary reports.
Answer: E,F
Explanation:
Performing static code analysis of committed code and continuously monitoring code commits to repositories can help detect unauthorized insertions into application development environments.
Static code analysis is a technique that involves analyzing code without executing it to identify potential vulnerabilities, security flaws, or other issues. By performing static code analysis of committed code and generating summary reports, the home automation company can identify any code that does not meet its standards or that may be malicious.
NEW QUESTION # 130
A security engineer needs to implement a cost-effective authentication scheme for a new web-based application that requires:
*Rapid authentication
*Flexible authorization
*Ease of deployment
*Low cost but high functionality
Which of the following approaches best meets these objectives?
- A. TACACS+
- B. SAML
- C. OAuth
- D. EAP
- E. Kerberos
Answer: C
Explanation:
OAuth, which stands for Open Authorization, is a standard for authorization that enables secure token-based access. It allows users to grant a web application access to their information on another web application without giving them the credentials for their account. OAuth is particularly useful for rapid authentication, flexible authorization, ease of deployment, and offers high functionality at a low cost, making it an ideal choice for new web-based applications. This approach is well-suited for situations where web applications need to interact with each other on behalf of the user, without sharing user's password, such as integrating a geolocation application with Facebook. OAuth uses tokens issued by an authorization server, providing restricted access to a user's data, which aligns with the objectives of rapid authentication, flexible authorization, ease of deployment, and cost-effectiveness.
NEW QUESTION # 131
Ann, a security manager, is reviewing a threat feed that provides information about attacks that allow a malicious user to gain access to private contact lists. Ann receives a notification that the vulnerability can be exploited within her environment. Given this information, Ann can anticipate an increase in:
- A. SQL injections attacks
- B. vishing attacks
- C. web application attacks
- D. brute-force attacks
Answer: A
NEW QUESTION # 132
A security analyst is evaluating all third-party software an organization uses. The analyst discovers that each department is violating the organization's policy by provisioning access to SaaS products without oversight from the security group and without using a centralized access control methodology. Which of the following should the organization use to enforce its SaaS product access requirements?
- A. SAML
- B. TACACS
- C. SLDAP
- D. VDI
Answer: A
Explanation:
Comprehensive and Detailed Step by Step
SAML (Security Assertion Markup Language)is a standard for single sign-on (SSO) that provides centralized authentication and authorization, ensuring SaaS access is governed by organizational policies.
SLDAP (Secure LDAP)focuses on directory services but does not centralize SaaS product access.
VDI (Virtual Desktop Infrastructure)is unrelated to SaaS authentication.
TACACS (Terminal Access Controller Access-Control System)is more suited for network devices.
Reference:
CompTIA CASP+ Exam Objective 2.3: Implement authentication and authorization technologies.
CASP+ Study Guide, 5th Edition, Chapter 6, Identity and Access Management.
NEW QUESTION # 133
A large industrial system's smart generator monitors the system status and sends alerts to third- party maintenance personnel when critical failures occur. While reviewing the network logs, the company's security manager notices the generator's IP is sending packets to an internal file server's IP. Which of the following mitigations would be BEST for the security manager to implement while maintaining alerting capabilities?
- A. Isolation
- B. Containment
- C. Segmentation
- D. Firewall whitelisting
Answer: C
NEW QUESTION # 134
A company hired a third party to develop software as part of its strategy to be quicker to market. The company's policy outlines the following requirements:
https://i.postimg.cc/8P9sB3zx/image.png
The credentials used to publish production software to the container registry should be stored in a secure location.
Access should be restricted to the pipeline service account, without the ability for the third-party developer to read the credentials directly.
Which of the following would be the BEST recommendation for storing and monitoring access to these shared credentials?
- A. MFA
- B. Local secure password file
- C. Key vault
- D. TPM
Answer: C
NEW QUESTION # 135
An engineer has had scaling issues with a web application hosted on premises and would like to move to a serverless architecture. Which of the following cloud benefits would be best to utilize for this project?
- A. Eliminating need to patch
- B. Automation of resource provisioning
- C. Cost savings for hosting
- D. Providing geo-redundant hosting
Answer: B
NEW QUESTION # 136
A security analyst is investigating a possible buffer overflow attack. The following output was found on a user's workstation:
graphic.linux_randomization.prg
Which of the following technologies would mitigate the manipulation of memory segments?
- A. DEP
- B. NX bit
- C. ASLR
- D. HSM
Answer: C
Explanation:
https://eklitzke.org/memory-protection-and-aslr
NEW QUESTION # 137
A security architect is analyzing an old application that is not covered for maintenance anymore because the software company is no longer in business. Which of the following techniques should have been implemented to prevent these types of risks?
- A. Code reviews
- B. Supply chain visibility
- C. Software audits
- D. Source code escrows
Answer: D
Explanation:
A source code escrow is a legal agreement that involves a third party holding the source code of a software application on behalf of the software vendor and the software licensee. The source code escrow ensures that the licensee can access the source code in case the vendor goes out of business, fails to provide maintenance or support, or breaches the contract terms. A source code escrow would have prevented the risk of having an old application that is not covered for maintenance anymore because the software company is no longer in business, because it would:
Allow the licensee to obtain the source code and continue to update, fix, or modify the application according to their needs.
Protect the vendor's intellectual property rights and prevent unauthorized disclosure or use of the source code.
Provide a legal framework and a trusted mediator for resolving any disputes or issues between the vendor and the licensee.
NEW QUESTION # 138
Which of the following allows computation and analysis of data within a ciphertext without knowledge of the plaintext?
- A. Homomorphic encryption
- B. Quantum computing
- C. Asymmetric cryptography
- D. Lattice-based cryptography
Answer: A
Explanation:
Reference: https://searchsecurity.techtarget.com/definition/cryptanalysis Homomorphic encryption is a type of encryption that allows computation and analysis of data within a ciphertext without knowledge of the plaintext. This means that encrypted data can be processed without being decrypted first, which enhances the security and privacy of the data. Homomorphic encryption can enable applications such as secure cloud computing, machine learning, and data analytics.References:
https://www.ibm.com/security/homomorphic-encryption
https://www.synopsys.com/blogs/software-security/homomorphic- encryption/
NEW QUESTION # 139
An energy company is required to report the average pressure of natural gas used over the past quarter. A PLC sends data to a historian server that creates the required reports.
Which of the following historian server locations will allow the business to get the required reports in an ## and IT environment?
- A. Use a screened subnet between the ## and IT environments.
- B. In the ## environment, allow IT traffic into the ## environment.
- C. In the ## environment, use a VPN from the IT environment into the ## environment.
- D. In the IT environment, allow PLCs to send data from the ## environment to the IT environment.
Answer: A
Explanation:
A screened subnet is a network segment that separates two different environments, such as ## (operational technology) and IT (information technology), and provides security controls to limit and monitor the traffic between them. This would allow the business to get the required reports from the historian server without exposing the ## environment to unnecessary risks. Using a VPN, allowing IT traffic, or allowing PLCs to send data are less secure options that could compromise the ## environment. Verified References:
https://www.comptia.org/blog/what-is-operational-technology https://partners.comptia.org/docs/default-source/resources/casp-content-guide
NEW QUESTION # 140
......
The CompTIA CAS-004 exam consists of 90 multiple-choice and performance-based questions, which must be completed within 165 minutes. CAS-004 exam is available in English, Japanese, and Portuguese, and is delivered through Pearson VUE testing centers worldwide. The passing score for the CASP+ exam is 750 on a scale of 100-900.
100% Reliable Microsoft CAS-004 Exam Dumps Test Pdf Exam Material: https://www.vcedumps.com/CAS-004-examcollection.html
Based on Official Syllabus Topics of Actual CompTIA CAS-004 Exam: https://drive.google.com/open?id=1ng6Ms5WLKJvbT5iZByrvY5jRBI555pmA
